
Lumi Loglake is now generally available in Imply Lumi


Search unstructured logs in place in your data lake
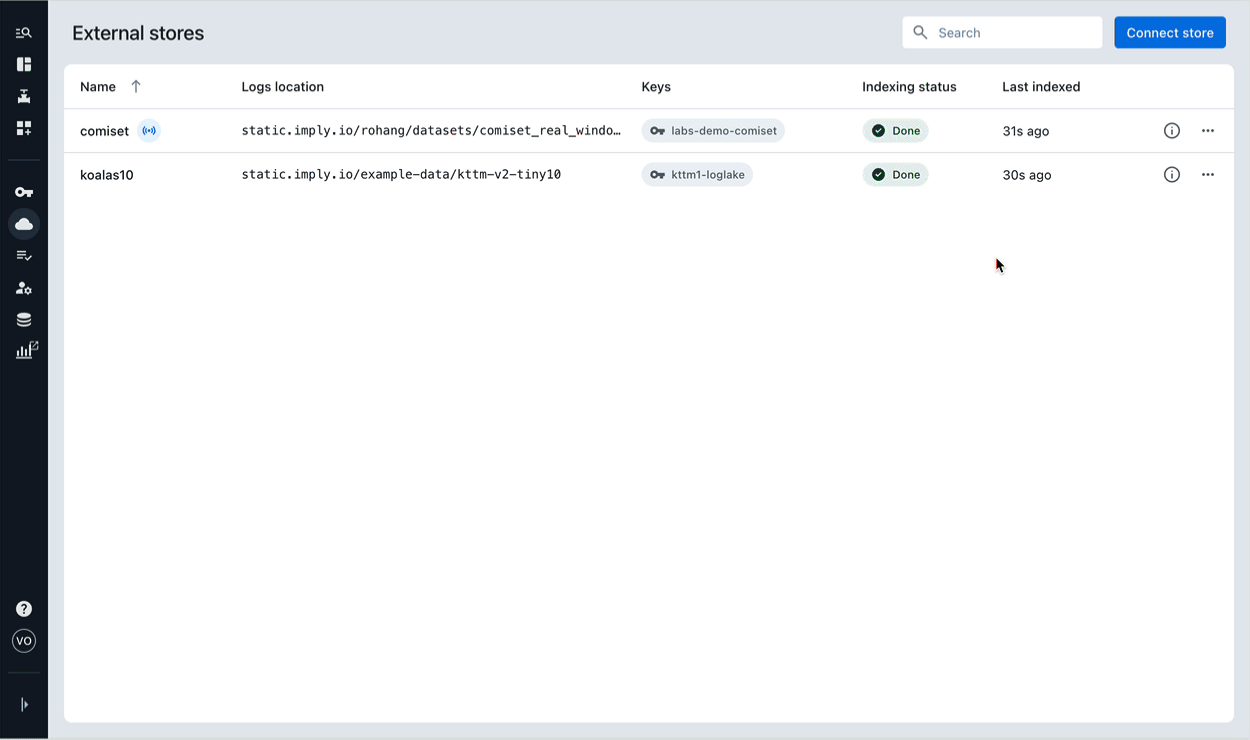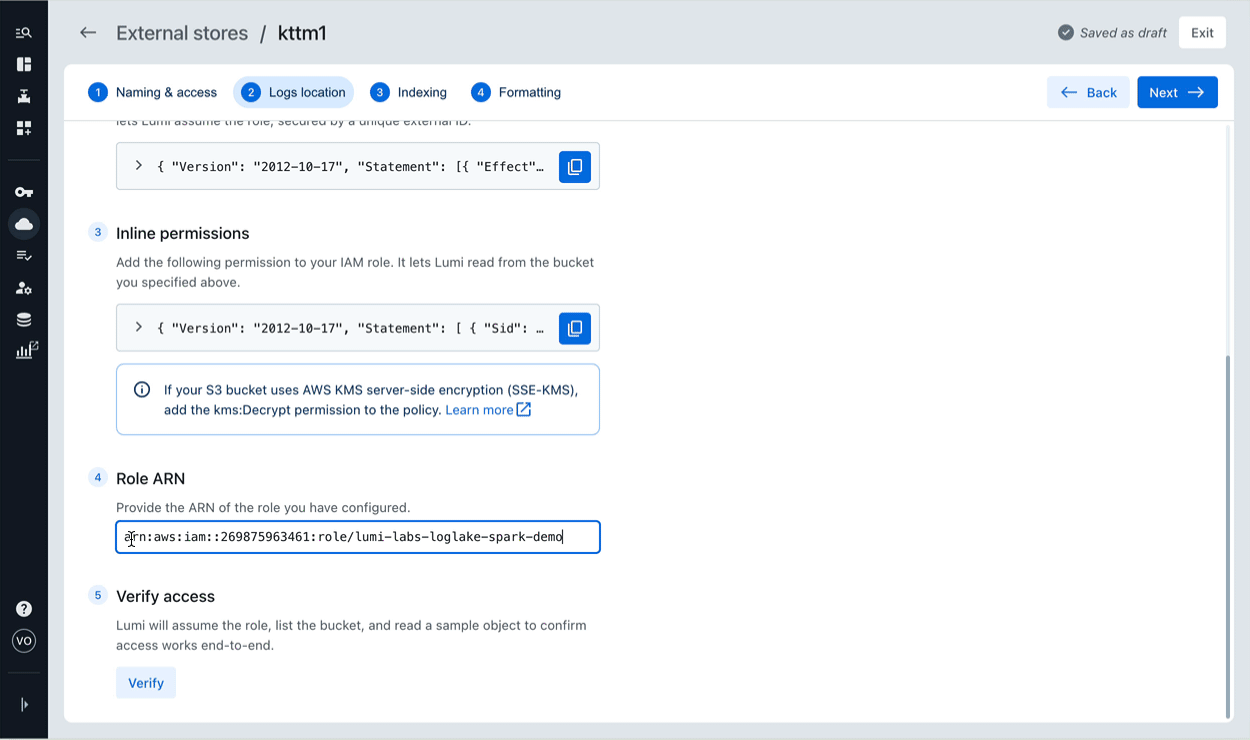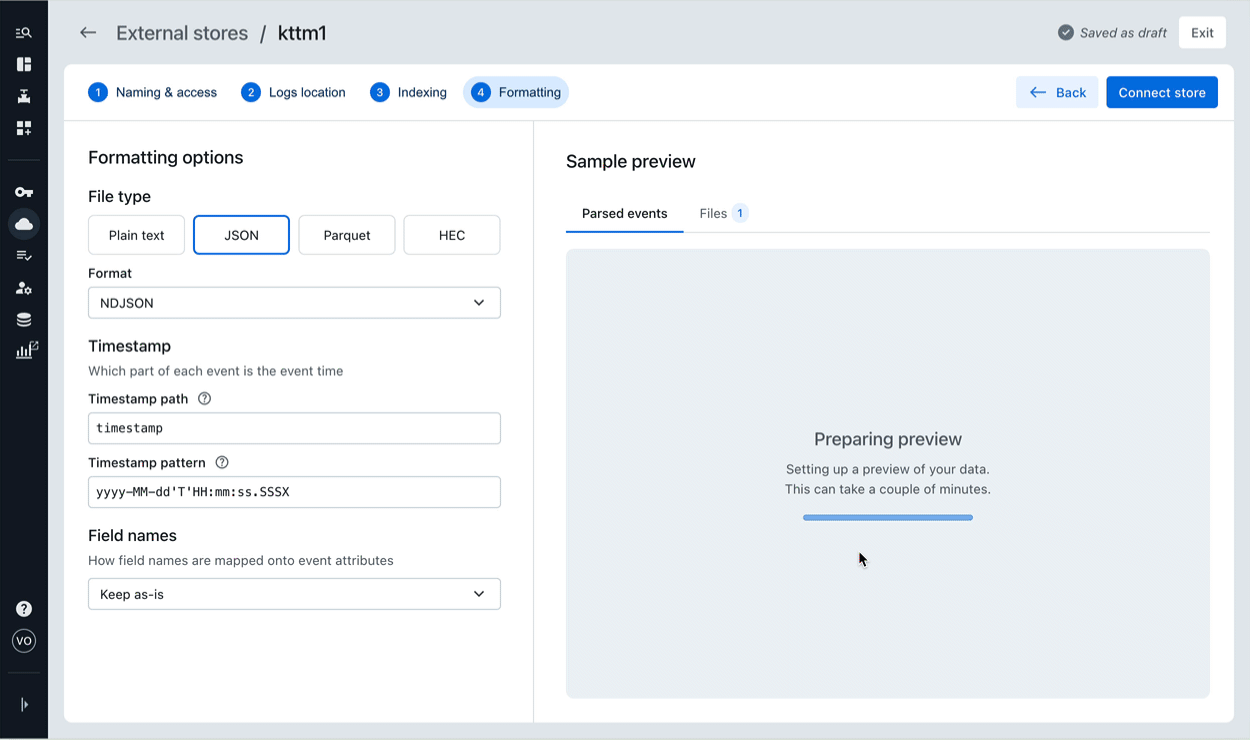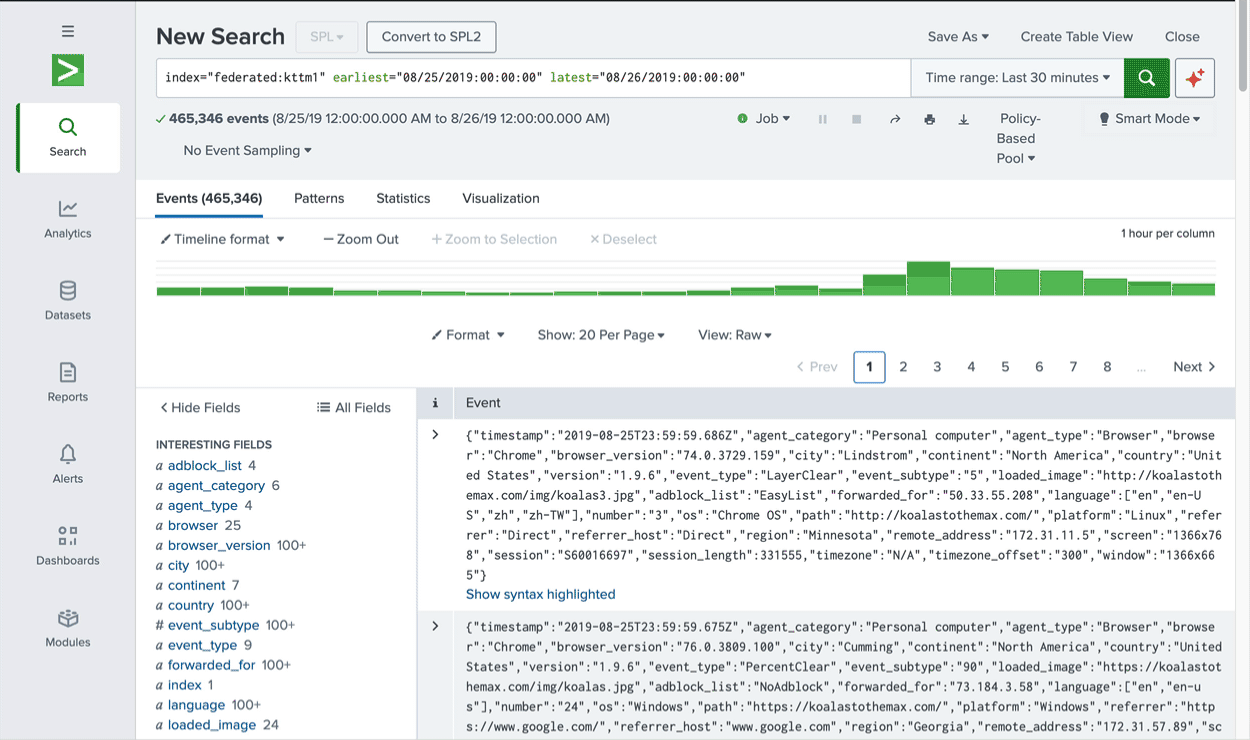
Today we’re announcing the general availability of Lumi Loglake, which lets Lumi search unstructured logs directly in data lakes via SPL and SQL without needing any schema management, data catalogs, or rehydration.
Loglake versus alternatives
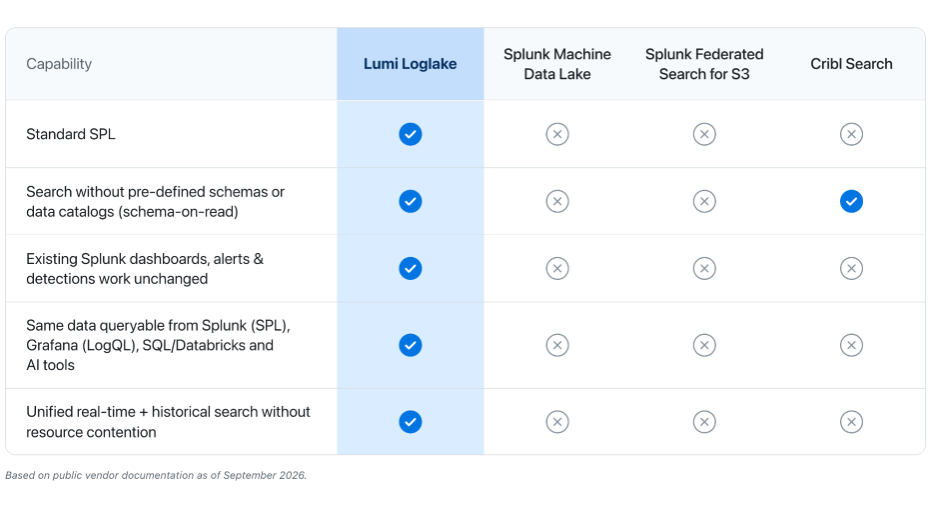
For a deeper look at how Loglake differs from other approaches, please see:
- Lumi Loglake vs. Splunk Federated Search
- Splunk SmartStore vs. Lumi Loglake
- Why logs in object storage don’t need a data catalog
Point Lumi at your logs. Start querying.
Loglake is designed to work with all popular data lakes including Amazon S3, Google Cloud Storage, Azure Cloud Storage, and more. Logs can be fully unstructured, or organized in data catalogs such as Apache Iceberg or Delta Lake. Logs can also be in any format such as text, Parquet, JSON, and GZIP.
It’s really as simple as pointing Lumi at your logs and querying your data. For the first time, security teams are not forced to first rehydrate, index, catalog, and model the data. Loglake fully supports schema-on-read, so there’s no need for predefined schemas, separate data catalogs, or data pipelines before an investigation can kick off.
For Splunk teams specifically, SOC analysts can search their data lake with standard SPL, and results come back as native Splunk events. Existing dashboards, alerts, detections, and applications, including Splunk Enterprise Security and Splunk SOAR, continue to work whether the data is indexed in Lumi or queried directly in object storage.
Historical and investigative searches also run on separate, on-demand compute pools. So a burst of investigative activity doesn’t eat into the resources real-time monitoring depends on. This means analysts can dig through months or years of data without slowing down the detections that are critical for protecting the business.
Put simply: you keep more telemetry in a cost-efficient data lake, and you search it right where it sits instead of moving or prepping it first. Your team keeps using the tools and workflows it already knows. And because compute scales independently, real-time monitoring, investigations, and AI workloads can all run at their own pace without competing for the same resources.
Loglake: query first. Optimize later.
Logs aren’t static business data. Formats shift, fields evolve, and new sources show up whether you planned for them or not. During an investigation, you rarely know ahead of time which fields are going to matter.
Loglake takes the opposite approach from “prepare, then search.” Lumi applies schema at query time, so teams can search first, reconstruct context on the fly, and optimize later only if a workload actually calls for it. A log format changing doesn’t have to trigger another round of schema maintenance or pipeline rework.
That same access layer spans indexed data and data sitting in object storage. Splunk teams can use SPL across both, and the underlying data can also support Grafana, Databricks, SQL-based tools, and AI applications. (For more, see A First Look at Lumi Loglake: Query Logs Where They Live.)
Keep more data. Make it all useful.
A security data lake shouldn’t turn into just another archive. Its value comes from making more data available to analysts, detections, and AI agents without forcing anyone to move it, prepare it in advance, or give up the tools they already rely on.
With Loglake, Lumi queries security data where it actually lives and returns results through the interfaces your team already uses. Your logs stay economical to retain without becoming second-class data. Learn more in the Lumi docs about searching external data.
Headed to Splunk .conf this year? Stop by the Imply Lumi Lounge on September 15 to see Loglake in action, catch live Lumi demos, and talk with Imply’s technical experts. You’ll also hear how BTG Pactual cut security data costs by more than 70% without replacing Splunk. Food and drinks are on us! We’re set up directly across from the Colorado Convention Center.
Related articles
More from Imply on the same topic.

Search your Splunk DDSS archive without restoring it
Security teams often keep logs long after they have aged out of their SIEM platform’s searchable window. The data is there for investigations or audits, but accessing the data for insights can be complicated.

Claude makes dashboards now, Lumi is ready for them
This week Anthropic launched Claude Dashboards in beta. You connect a data source, ask a question in plain language, and Claude writes the queries and builds the dashboard.

Lumi Lounge Recap: 3 Takeaways from Splunk .conf26
The Imply Lumi Lounge sat directly across the street from Splunk .conf26 and reached venue capacity on both days. Digital signs around the Colorado Convention Center pointed attendees our way with a simple message: “Federated search, done right. Full SPL. Less spend.”

Agents don’t query like your detections do
A security team of four has run a major SIEM since February. Nobody on the team writes SPL. Nobody opens the console or looks at the dashboards. Every question goes through an AI agent, which writes the query, runs it, reads the result, and answers in plain language.

Why You Shouldn’t Have to Delete Your VPC Flow Logs
When a security incident happens, investigators almost always start with the same questions: Which systems communicated? Where did the traffic originate? What changed before the incident? Was data exfiltrated? AWS VPC Flow Logs are often the fastest way to answer those questions.

Splunk Smartstore vs Lumi Loglake: Two Very Different Ways to Search Logs in Object Storage
One copies data back before it can be searched. The other queries it where it lives. Lumi Loglake lets Splunk teams query logs directly in object storage, including AWS S3, Delta Lake, Apache Iceberg, using standard SPL.

Supercharging Schema-On-Read: Logs in Object Storage Don’t Need a Data Catalog
Machine data architectures are rapidly changing. As telemetry volumes continue to grow and as costs rise, organizations are increasingly moving logs and other machine data into object stores such as AWS S3.

Imply Lumi Loglake vs Splunk Federated Search for S3
Teams are increasingly moving log data into AWS S3 to reduce costs and extend retention. Both Lumi Loglake and Splunk Federated Search to S3 help you query data in AWS S3 to lower costs, however the two technologies have several notable differences.

A First Look at Lumi Loglake: Query Logs Where They Live
TL;DR: Imply Lumi Loglake is a lakehouse (separated compute/storage) architecture for unstructured logs that reduces costs from 40% up to orders of magnitude on your hardware/AWS/Azure bill used to run your SIEM/observability products.

Imply Lumi Major Release Preview: Continuing the Journey Towards Decoupled Observability/SIEM
We are getting ready to introduce the next major expansion of Imply Lumi and the observability warehouse. When we introduced the industry’s first observability warehouse, the goal was clear: decouple the observability stack by separating storage, compute, and access.

Query Lumi from Grafana: Now in Private Preview
Observability has a silo problem. Today, we’re removing another one. Imply Lumi’s Grafana Loki integration is now in Private Preview.

BTG Pactual + Imply Lumi: More Data. Longer Retention. Lower Cost. Without Replacing Splunk.
Most security teams are forced to choose between cost, retention, and performance as data volumes grow. BTG Pactual broke that tradeoff by rethinking the data layer underneath Splunk — without touching a single workflow.
